Symbiosis Exploit Highlights Bitcoin Bridge Risks Without Compromising Bitcoin
Key Takeaways
- •Symbiosis detected the attack at approximately 04:28 UTC and immediately suspended BTC routing while other routing protocols remained active.
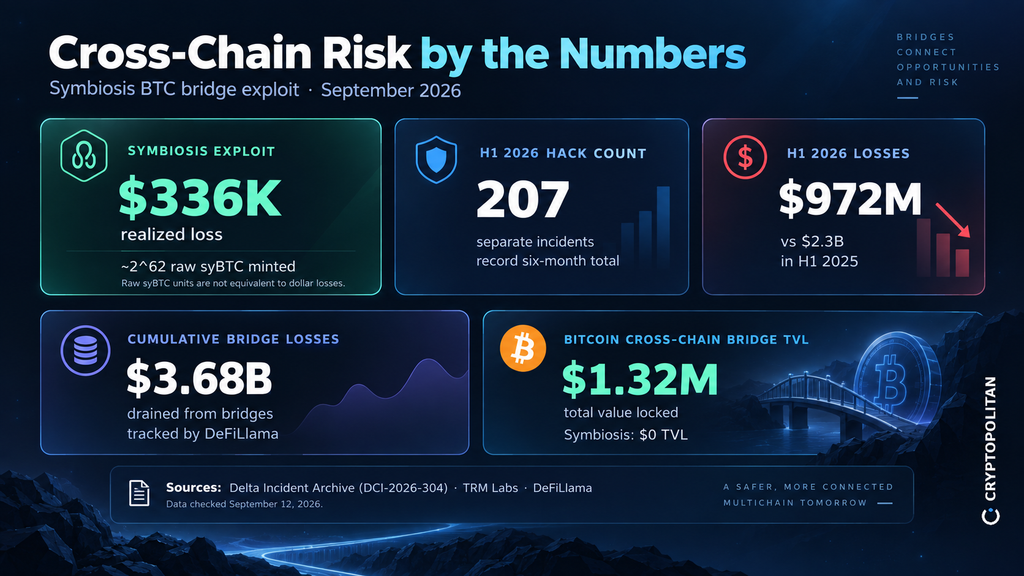
- •BridgeV2 generated more than 2^62 syBTC after processing an incorrect cross-chain message, but only about $336,000 in real assets was extracted.
- •The exploit affected Bitcoin bridge infrastructure rather than Bitcoin’s underlying network.
- •DeFiLlama estimates cumulative bridge losses of at least $3.68 billion, underscoring recurring security problems in cross-chain systems.
- •Symbiosis’s next steps include determining when BTC routing will resume and how BridgeV2’s message-authentication controls will be changed.
Symbiosis shut down its native Bitcoin bridge on Friday after an attacker exploited its BridgeV2 contract to mint a huge amount of unbacked synthetic BTC. However, the attacker extracted only about $336,000 in real value. Symbiosis disclosed the incident on X.
The gap between the scale of the synthetic mint and the realized loss is significant. Bitcoin itself was not compromised. Instead, the vulnerability affected infrastructure that moves BTC into decentralized finance (DeFi). The incident came only days after a breach of the Liquid Network that caused an estimated $320 million loss, renewing questions about the security of cross-chain systems even as Bitcoin’s base network remains unaffected.
BTC routes halted while other services remained open
Symbiosis said it found evidence of the Bitcoin Bridge attack on September 11 at approximately 04:28 UTC and immediately halted BTC routing. Other routing protocols continued to operate.
The Delta Incident Archive classified the incident as DCI-2026-304. According to the archive, BridgeV2 processed an incorrect message that caused more than 2^62 syBTC to be generated on BNB Chain and Ethereum.
The attacker converted part of the illegitimate balance into approximately 4.39 WBTC on Ethereum, generating about $336,000 in proceeds. DeFiLlama classifies the incident as an “Unbacked Cross-Chain Mint.”
How cross-chain trust enters the system
Symbiosis documentation describes a bridge architecture that depends on the secure transmission and authentication of cross-chain messages.
BridgeV2 connects the protocol’s Portal and Synthesis contracts to its off-chain Relayers Network. The relayers submit transactions signed using a Multi-Party Computation (MPC) key stored in the contract.
Through MPC threshold signatures, native Bitcoin is secured in a Portal. Relayers can then create syBTC on another blockchain, where it is converted into the user’s preferred asset. Symbiosis has said that Decurity audited its native BTC bridge.
The model depends on accurate authentication of instructions transmitted between chains. In this incident, that authentication process failed. The result shows why bridge security involves both the custody of the underlying BTC and the controls governing issuance of its cross-chain representation.
Massive synthetic mint, limited realized loss
The minting of more than 2^62 raw syBTC should not be confused with the total amount stolen. Although the issuance created a massive accounting imbalance, the attacker converted only a small portion of the synthetic balance into real assets. The estimated loss is approximately $336,000.
That amount places the Symbiosis incident near the lower end of major crypto hacks recorded in 2026. TRM Labs reported 207 crypto hacks during the first half of the year, the highest semiannual total in its history. The average loss was $219,000. Aggregate losses fell from $2.3 billion in the first half of 2025 to $972 million in the first half of 2026.
Recurring failures across bridge infrastructure
The broader concern is the frequency with which cross-chain bridges continue to fail. DeFiLlama estimates total bridge losses of at least $3.68 billion. Symbiosis has identified weak message authentication as one recurring cause of bridge attacks.
The effects can extend beyond the bridge itself. An analysis by the Bank Policy Institute of the KelpDAO hack found that unbacked rsETH created through inadequate cross-chain validation contributed to stress on Aave. The incident led to the withdrawal of $5 billion worth of stablecoins, while the borrowing interest rate rose to 10%.
Echoes of the $320 million Liquid Network breach
The Symbiosis exploit followed a much larger failure on Liquid Network. Chainalysis reported that self-described white-hat hackers took 4,000 of Liquid’s 4,200 BTC, worth approximately $320 million, by exploiting a defect in cached transaction-validation proofs. The flaw enabled the creation of unbacked L-BTC, which was later exchanged for real Bitcoin.
Cryptopolitan reported earlier this week that the hackers returned 3,400 BTC, or about 85% of the lost funds.
Neither exploit compromised Bitcoin’s underlying network. Both exposed weaknesses in systems built around it.
For users and operators, the immediate issues to monitor are whether Symbiosis resumes BTC routing and what changes it makes to BridgeV2’s message-authentication process. The current data also highlights the limited scale of Bitcoin bridge liquidity: DeFiLlama’s Bitcoin cross-chain bridge data shows about $1.32 million in total value locked across the sector, while Symbiosis is listed at $0.
The issue extends beyond Symbiosis. Continued incidents could affect the movement of BTC into DeFi, leaving liquidity in separate ecosystems and making cross-chain services appear riskier and less attractive.

