Binance's Richard Teng Says Attack Went Beyond a Single Engineer's Permissions
Key Takeaways
- •Binance's Richard Teng said on October 30, 2026, that the reported attack went beyond the permissions available to any single engineer.
- •Teng rejected characterizations of the incident as a simple one-click action, describing such labels as inaccurate.
- •The clarification does not confirm whether multiple employee accounts were compromised or establish exactly how the attackers operated.
- •The statement does not specify the attack's financial impact or confirm that customer funds were affected.
- •A detailed incident report from Binance could clarify the attack's entry points, affected systems, and remediation measures.
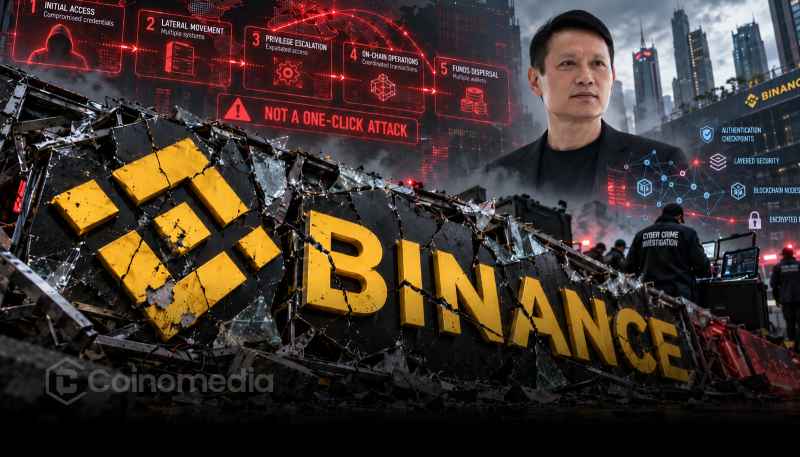
Binance's Richard Teng has clarified that the recently reported attack went beyond the permissions available to any single engineer, rejecting characterizations of the incident as a simple “one-click” action.
His comments challenge the notion that one employee could have triggered the entire incident through a single authorized action, and they raise fresh questions about the attack's complexity — although its full technical details remain unclear. In an industry where centralized exchanges hold custody of customer assets and account data, the precise scope of a security incident is often among the most closely scrutinized details, which helps explain why executive clarifications draw significant attention.
Clarification Challenges “One-Click” Claims
In remarks circulated on October 30, 2026, Teng addressed the claims surrounding the incident, explaining that it was more complex than some descriptions suggested. According to Teng, the attack exceeded the permissions available to a single engineer and cannot accurately be described as a one-click action.
Simplified labels like “one click” often circulate while an incident is still developing, which is why statements from a company's leadership are typically treated as the reference point for what has actually been confirmed. The clarification suggests that understanding the event requires a closer examination of the permissions, systems, and actions involved. However, the statement does not identify the complete attack sequence or establish exactly how the attackers operated. It also does not confirm whether multiple employee accounts were compromised.
These distinctions matter: an attack that exceeds one engineer's permissions does not necessarily prove that several engineers participated. For now, Teng's explanation provides additional context without resolving every question about the incident.
UPDATE: Binance’s Richard Teng clarifies the attack went beyond one engineer’s permissions and was not a “one-click” action. pic.twitter.com/eBfmesTVQD — Cointelegraph (@Cointelegraph) October 30, 2026
Why the Distinction Matters
The clarification highlights an important aspect of cybersecurity: the difference between an employee's authorized permissions and an attacker's actual capabilities. Large cryptocurrency platforms typically use access controls to limit what individual employees can do within sensitive systems. These controls are designed to reduce the potential damage caused by compromised credentials or unauthorized activity, and permission-based access systems of this kind are a standard feature of enterprise security well beyond the crypto sector.
Attackers, however, may attempt to exploit weaknesses across multiple systems, accounts, or security processes. An incident that exceeds one person's permissions could therefore involve a more complicated sequence than a single account action.
That said, Teng's comments alone do not establish which security controls were involved or whether any particular system failed. The distinction matters for users trying to understand the risks associated with centralized cryptocurrency platforms. Reducing an incident to a one-click explanation can omit important technical details, and accurate reporting requires separating confirmed statements from assumptions about how an attack occurred.
What Happens Next for Binance Security?
Following Teng's clarification, attention may turn toward whether Binance releases further technical information. A detailed incident report could help clarify how the attack developed, which permissions were involved, and which safeguards were activated. Such information would also help users distinguish between an isolated security event and a broader operational concern. Post-incident disclosures from exchanges commonly outline entry points, affected systems, and remediation measures, so the depth of any future Binance statement will shape how complete the public picture becomes.
For cryptocurrency exchanges, transparent communication is important because customers rely on these platforms to safeguard digital assets and sensitive account information. The available statement does not specify the financial impact of the attack or confirm that customer funds were affected. It would therefore be premature to draw conclusions about losses, employee involvement, or the effectiveness of Binance's wider security infrastructure. In the meantime, users generally rely on an exchange's official channels rather than secondhand summaries when verifying updates about an active incident.
For now, Teng's central message stands: the attack cannot accurately be reduced to one engineer's permissions or a single click. Further verified details will be necessary to establish the incident's full scope, its financial impact, and how it unfolded.

