$6 Million Drained From Base Vault Controlled by Unidentified 7-Signer Safe
Key Takeaways
- •A newly created contract added to the vault's whitelist borrowed 1,783.067 aBaswstETH receipt tokens and redeemed them through Aave on Base for roughly 1,783 wstETH, in six separate outflows counted by Exvul.
- •The vault's operating owner is a 3-of-7 Safe multisignature wallet created about 324 days ago, but neither the Safe nor any of its seven signer addresses has been publicly identified, and no protocol has claimed the vault.
- •Security firms have not confirmed the precise authorization failure, and the incident did not involve a compromise of the Base chain itself or of any confirmed core contract.
- •Losses exceeded $6 million within roughly 40 minutes of detection, after about $2.02 million had already left the contract when Blockaid flagged the exploit.
- •Systemic risk appears contained for now, but the disposal of the stolen wstETH, a widely used collateral asset in decentralized-finance lending, could put near-term pressure on its peg.
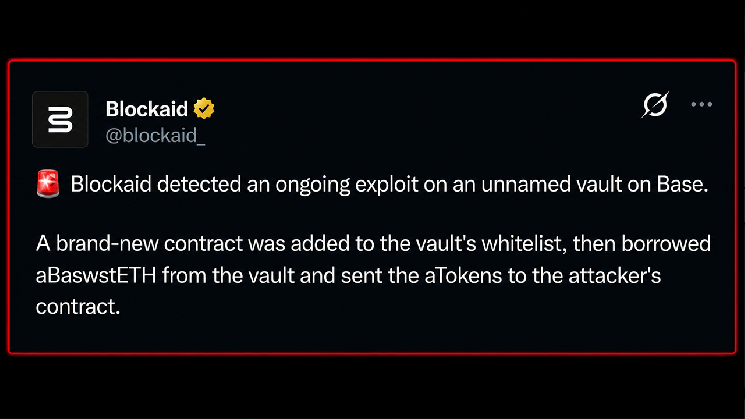
At 09:21 UTC on Oct. 4, security firm Blockaid detected what appeared to be an active exploit targeting a vault on Base, Coinbase's Ethereum layer-2 network. By then, roughly $2.02 million had already left the contract. Within about 40 minutes, losses had climbed past $6 million, with security researchers tracing approximately 1,783 wstETH out of the vault.
Adding to the intrigue, no protocol has come forward to claim ownership. The vault's apparent controller is a 3-of-7 Safe multisignature wallet whose seven signers remain unidentified, leaving a multimillion-dollar crime scene without a publicly known owner. Safes of this kind are a staple of onchain operations — shared contract wallets that require several distinct keys to approve a single transaction, commonly used to hold protocol treasuries and admin controls.
Six Outflows, One Newly Whitelisted Contract
PeckShield, CertiK and Exvul arrived at broadly the same tally. According to the security firms, 1,783.067 aBaswstETH — Aave receipt tokens representing wrapped staked ether deposited on Base — was borrowed from the vault and redeemed through Aave on Base into about 1,783 wstETH.
In practice, a newly created contract was added to the vault's whitelist, borrowed those receipt tokens, transferred them to an attacker-controlled contract and redeemed them through Aave for the underlying wstETH. Exvul counted six separate outflows.
The precise authorization failure, however, remains unconfirmed. Security firms have not said that any core contracts were compromised, and this was not a hack of the Base chain itself. Speculation about a compromised wallet or a particular Aave position remains exactly that — speculation. Until a confirmed account emerges, the central open question is how a freshly created contract came to be whitelisted at the vault in the first place.
A Seven-Signer Safe With No Name
Onchain records deepen the mystery. The drained vault is an OpenZeppelin transparent proxy whose owner points to a Safe created roughly 324 days ago. That Safe requires three of seven signatures to act — a threshold design intended to ensure that no single compromised key can move funds on its own — but it carries no public protocol name, and none of its seven signer addresses has been publicly identified by the security firms tracking the incident.
Upgrade authority is separate, adding another layer of contracts between the vault and whoever ultimately controls it. For now, the operating owner visible onchain is the anonymous 3-of-7 Safe. The drained proxy is 0xD1895f2019c2152FC2b9022D57f19198c4CFCABC, while its Safe owner is 0x6b27512a5943Ed327f6cb6C3EC1f0398229f42C4. Basescan and Arkham Intelligence identify the latter as a Safe proxy created through Safe Proxy Factory 1.4.1.
The distinction matters for understanding what investigators actually know. They can see the vault, its owner contract, the seven signing addresses and the token trail. What they cannot see is the human organization behind those addresses, or whether the whitelist change stemmed from stolen credentials, a white hat hacker, faulty permissions or another unknown weakness. No public team has stepped forward to fill in the blank.
Systemic risk appears contained for now, though unloading the stolen wstETH — Lido's wrapped liquid-staking token, widely used as collateral across decentralized-finance lending markets — could put near-term pressure on its peg. What remains is a curious tableau: roughly $6 million gone, onchain investigators able to trace the machinery behind the drain, and seven signer addresses sitting in plain sight — while the people controlling those addresses remain conspicuously absent from the story.
This story is still developing. No protocol has claimed the vault, and no one has published a confirmed account of a bug or key compromise. Among the open items worth watching: any disclosure identifying the Safe's signers or the protocol behind the vault, security firms' confirmation of how the whitelist change was authorized, and any further movement of the redeemed wstETH onchain. More details will be added as new information emerges.

