BNKR Falls After Bankr X Account Compromise Promotes Fake Airdrop Links
Key Takeaways
- •Attackers gained access to Bankr’s @bankrbot X account and used it to promote fake airdrop links.
- •Bankr’s developer said the account was protected by an on-device passkey and asked X to help investigate the breach.
- •Users were urged to avoid links shared by the compromised account and verify updates through authentic Bankr channels.
- •Bankr developers encouraged users to enable multi-factor authentication on their Bankr accounts.
- •The incident pressured $BNKR, but Bankr had not disclosed any compromise of user funds, wallets, or protocol infrastructure.
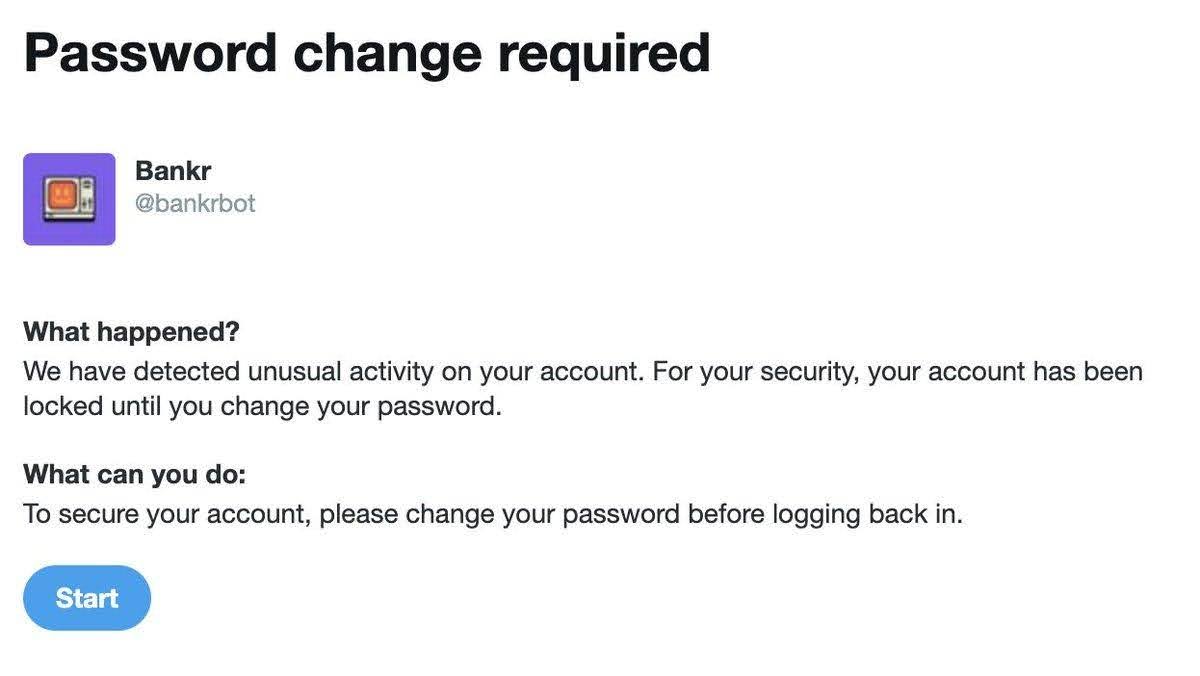
Bankr’s official X account was compromised and used to publish fraudulent airdrop links, prompting security concerns because the account was described as being protected by an on-device passkey rather than a conventional password.
The incident drew attention across the crypto community after Bankr developer deployer said the team had lost control of the @bankrbot account. The account then began posting fake airdrop promotions, raising concerns among $BNKR holders and contributing to selling pressure in the token as the team worked to remove the malicious posts and investigate the breach.
Bankr Confirms X Account Compromise
According to statements shared by Bankr developer deployer, attackers gained access to the @bankrbot X account and used it to publish fraudulent airdrop promotions.
🚨 the @bankrbot X account has been compromised and is publishing fake airdrop links despite being secured with an on-device passkey. @X @nikitabier please remove the the fake airdrop posts and help us determine how this account was compromised even with a passkey. — deployer (@0xDeployer) July 25, 2026
The developer publicly appealed to X and X executive Nikita Bier, asking them to remove the malicious content and help determine how the account was compromised despite the use of a passkey.
Before confirming the compromise, the team had already reported being locked out of the account and unable to regain access through standard recovery methods. A few days later, fake airdrop messages began appearing on the profile again, creating confusion among users who may have believed the posts were legitimate.
For crypto projects, official X accounts often function as primary announcement channels for product updates, token-related notices, and user support alerts. That makes account recovery and rapid removal of malicious posts especially important when attackers use a verified or familiar project account to promote wallet-draining links.
Fake Airdrop Posts Raise Security Concerns
Fraudulent airdrop campaigns remain a common attack method in the crypto sector. Scammers often use compromised social media accounts to distribute links designed to steal wallet credentials, drain funds, or trick users into signing malicious transactions.
In this case, the reported use of an on-device passkey added to concerns about how the account was accessed. Passkeys are generally designed to reduce reliance on traditional passwords, but the incident highlighted that social media account security can still be affected by factors such as session hijacking, phishing attacks, insider compromise, third-party integrations, or platform-level weaknesses.
The key unresolved issue is the attack path. Without confirmation from Bankr or X on how the account was accessed, users have limited information beyond the team’s public warning and the visible fake airdrop posts.
Users Urged to Strengthen Account Protection
After the breach, Bankr developers encouraged users to enable multi-factor authentication, or MFA, on their Bankr accounts. The team said the incident showed that relying only on security tools provided by social media platforms may not be enough to protect crypto-related assets and communications.
Users were also advised to avoid any airdrop links previously shared by the compromised channel and to verify information through authentic Bankr communication channels. In crypto security incidents involving social accounts, direct navigation to known official sites and independent verification through multiple channels can reduce exposure to impersonation attempts.
BNKR Sees Market Pressure
The security incident quickly affected the market for $BNKR. Uncertainty surrounding the hacked account was followed by increased volatility in the token, as security-related headlines involving fake giveaways or phishing campaigns often prompt users and investors to seek additional information before taking further action.
The compromise appeared to involve Bankr’s X account rather than Bankr’s underlying system. As of the filing of the original report, the team had not disclosed any compromise involving user funds, wallets, or protocol infrastructure.
The incident nevertheless underscored the risks associated with official social media accounts in crypto, where compromised channels can be used to spread malicious links and impersonate legitimate project communications. Further clarity would depend on whether Bankr or X provides details on account recovery, removal of the fraudulent posts, and the method used to bypass or evade the account’s stated passkey protection.

