Researchers Forge 1024-bit RSA Signature Without Extracting Private Key
Key Takeaways
- •Researchers at UC San Diego and Inria forged a 1024-bit RSA signature without extracting the private key, using about 4.3 billion queries to a raw, unpadded signing oracle on a hardware security module.
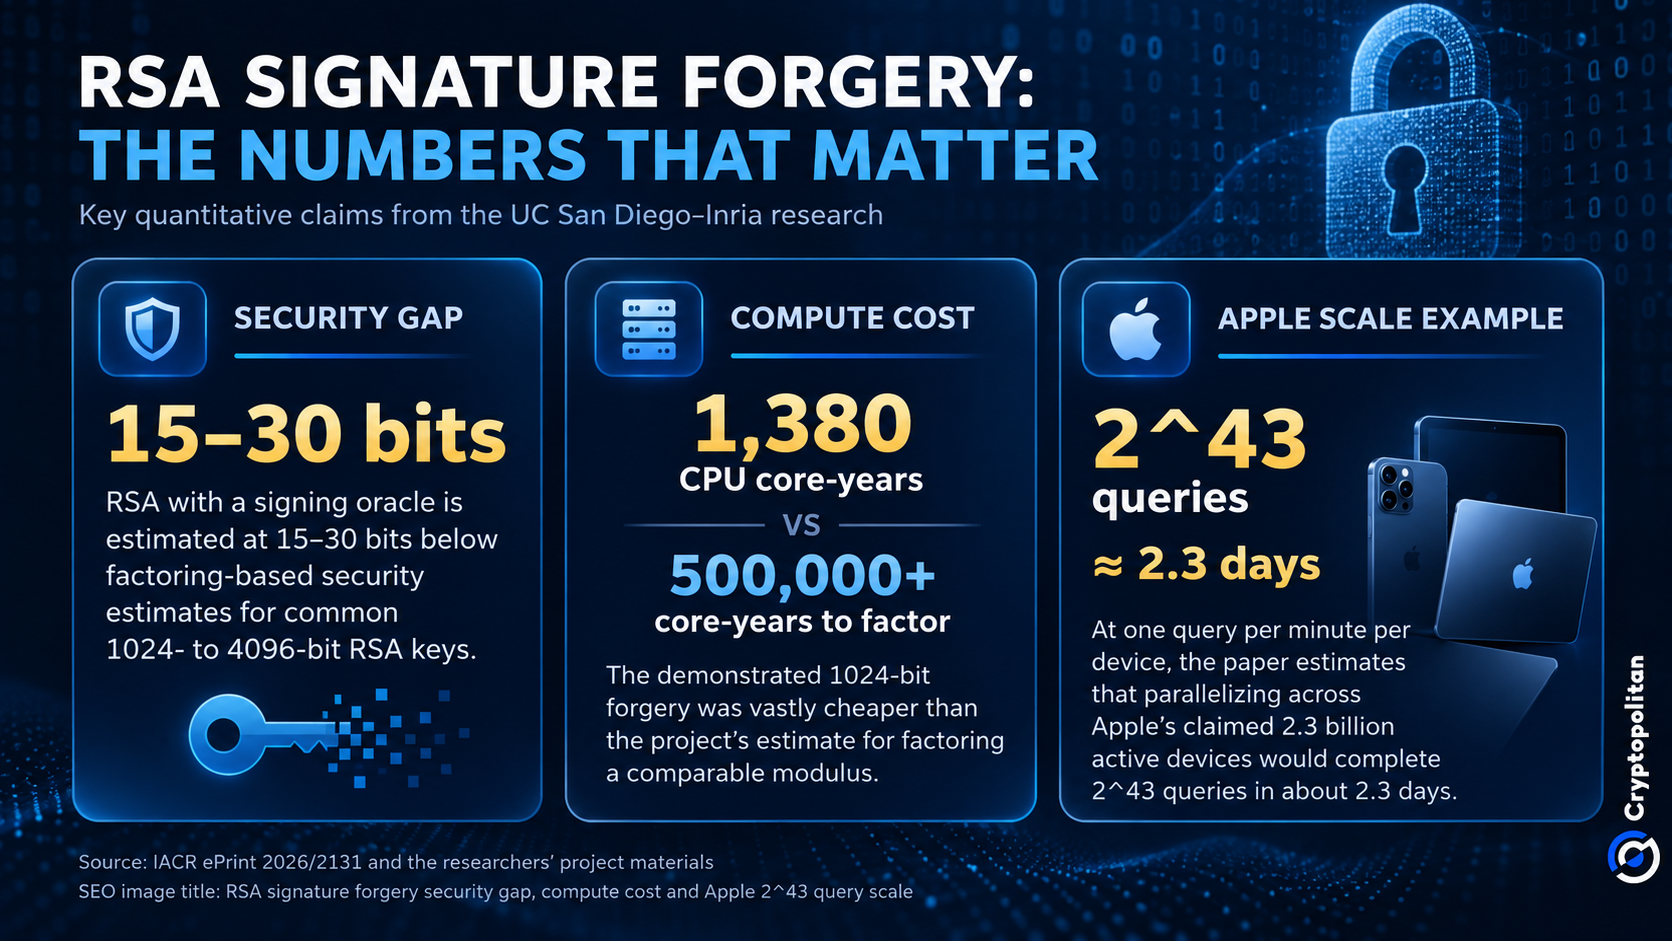
- •The attack consumed 1,380 CPU core-years over five months, far less than the 500,000 to 1,000,000 core-years estimated to factor the same key, and follow-up forgeries should cost around 180 core-years after precomputation.
- •The technique requires a raw, unpadded RSA signing interface, so standard PKCS#1 v1.5 and RSA-PSS signatures are not practically vulnerable, and Bitcoin and Ethereum, which rely on secp256k1 ECDSA and Schnorr signatures, are unaffected.
- •The 1024-bit key size has been disallowed by NIST for digital signatures since 2013, and the underlying algorithm dates to 2007, with the researchers' practical implementation being the novel element.
- •For crypto custodians, the finding shows that secure hardware alone is insufficient if signing APIs and approval workflows are compromised, a risk reflected in EY's 2026 survey and ESMA's July 8 supervisory action on key and storage management.
A team of researchers at UC San Diego has demonstrated that a 1024-bit RSA signature can be forged by sending large volumes of queries to a hardware security module (HSM) — a hardened device built to generate and store cryptographic keys while keeping the key material isolated inside — without ever extracting the private key from the device.
The finding points to a distinct category of risk for crypto custodians: storing a key inside tamper-proof hardware is not sufficient on its own if an attacker compromises the systems that are authorized to use it.
Forging a signature the key never signed
In IACR ePrint 2026/2131, Laura Shea, Miro Haller, Adam Suhl, and Nadia Heninger of UC San Diego, together with Emmanuel Thomé of Inria, describe how temporary access to a raw RSA signing oracle — an interface that signs arbitrary data exactly as submitted, without applying any padding — can ultimately enable an attacker to forge signatures offline.
The attack involved 2^32 basic signing requests — slightly more than 4.3 billion queries — consuming 1,380 CPU core-years of computing time spread across five calendar months. By comparison, according to the researchers' project materials, factoring the same 1024-bit RSA modulus would take approximately 500,000 to 1,000,000 core-years. Most of that work is performed only once, during precomputation; afterwards, forging a chosen signature should require around 180 core-years.
The 1024-bit target is itself dated: NIST guidance has disallowed 1024-bit RSA keys for generating digital signatures since 2013.
The underlying algorithm dates back to 2007. What has changed is that the team actually carried out the attack in practice, as Bruce Schneier noted on September 28:
"What is new is the implementation." — Bruce Schneier
Why unpadded signing is the whole trick
A critical constraint applies to this type of attack: it requires access to a raw, unpadded RSA signing or decryption oracle. Standard RSA signatures using PKCS#1 v1.5 or RSA-PSS do not expose such an interface, so the technique does not constitute a practical attack on properly implemented RSA. That distinction matters well beyond this demonstration: RSA remains one of the most heavily deployed public-key algorithms, protecting TLS handshakes, code signing, and payment systems.
As Decrypt noted, the researchers disabled the certified FIPS mode — the configuration validated under U.S. federal cryptographic standards — on the HSM and used a test key of their own.
According to the paper, raw signing access can still surface in HSM APIs and in RSA blind-signature systems. The paper cites RFC 9474 as an example, describing a scenario in which a server signs a blinded message without ever seeing the original message.
To illustrate how quickly concurrent requests can accumulate, the study uses Apple's figure of 2.3 billion active devices. At one token per minute, a single device would need roughly 17 million years to reach 2^43 queries. Spread across 2.3 billion devices, however, the same number of requests could be submitted in about 2.3 days.
Signing interfaces as part of the perimeter
For crypto custodians, locking a private key in secure hardware does not deliver complete safety. The APIs, approval workflows, and automated systems that invoke the key carry their own risks.
The industry is already reflecting this concern. According to EY's 2026 survey, the security of digital assets and key-signing procedures has become far more significant in the custodian selection process. The Common Supervisory Action launched by ESMA on July 8 likewise focuses scrutiny on key and storage management, transaction controls, and incident response.
According to the researchers, RSA exposed to a signature oracle provides 15-30 bits less security than factoring-based estimates for typical keys of 1024 to 4096 bits. Under this model, 4096-bit RSA does not even deliver the security of 128-bit encryption.
Not a Bitcoin or Ethereum break
The research concerns RSA only. Ethereum uses secp256k1 ECDSA, while Bitcoin relies on secp256k1 ECDSA and Schnorr signatures, so the demonstrated attack does not apply to their transaction-signing systems.
The broader custody-risk issue, however, is not entirely new. A Cryptopolitan report on September 20 described how compromised signing authorities were used to drain roughly $2 million from Fetch.ai and NuNet. That case involved an individual obtaining the key itself; the new research shows that an attacker may instead gain signing authority without ever holding the key.

