How Public Key Cryptography Secures Crypto and the Internet
Key Takeaways
- •Public key cryptography employs mathematically linked key pairs—a freely shared public key and a guarded private key—to enable secure encryption, digital signatures, and authentication without requiring parties to exchange secrets beforehand.
- •RSA and elliptic-curve cryptography became the dominant algorithm families carrying public key cryptography into widespread commercial use, securing everything from HTTPS websites and email to software updates and cryptocurrency networks.
- •NIST released its first three finalized post-quantum encryption standards in August 2024—FIPS 203, FIPS 204, and FIPS 205—based on new mathematical approaches designed to resist quantum computing attacks.
- •Many government agencies plan to deprecate RSA-2048 and ECC P-256 by 2030–2035 because sufficiently powerful quantum computers could solve the mathematical problems these classical algorithms rely on.
- •The 'harvest now, decrypt later' threat allows adversaries to collect encrypted data today with the expectation of decrypting it once quantum capabilities mature, making the transition to post-quantum standards urgent even before large-scale quantum machines exist.
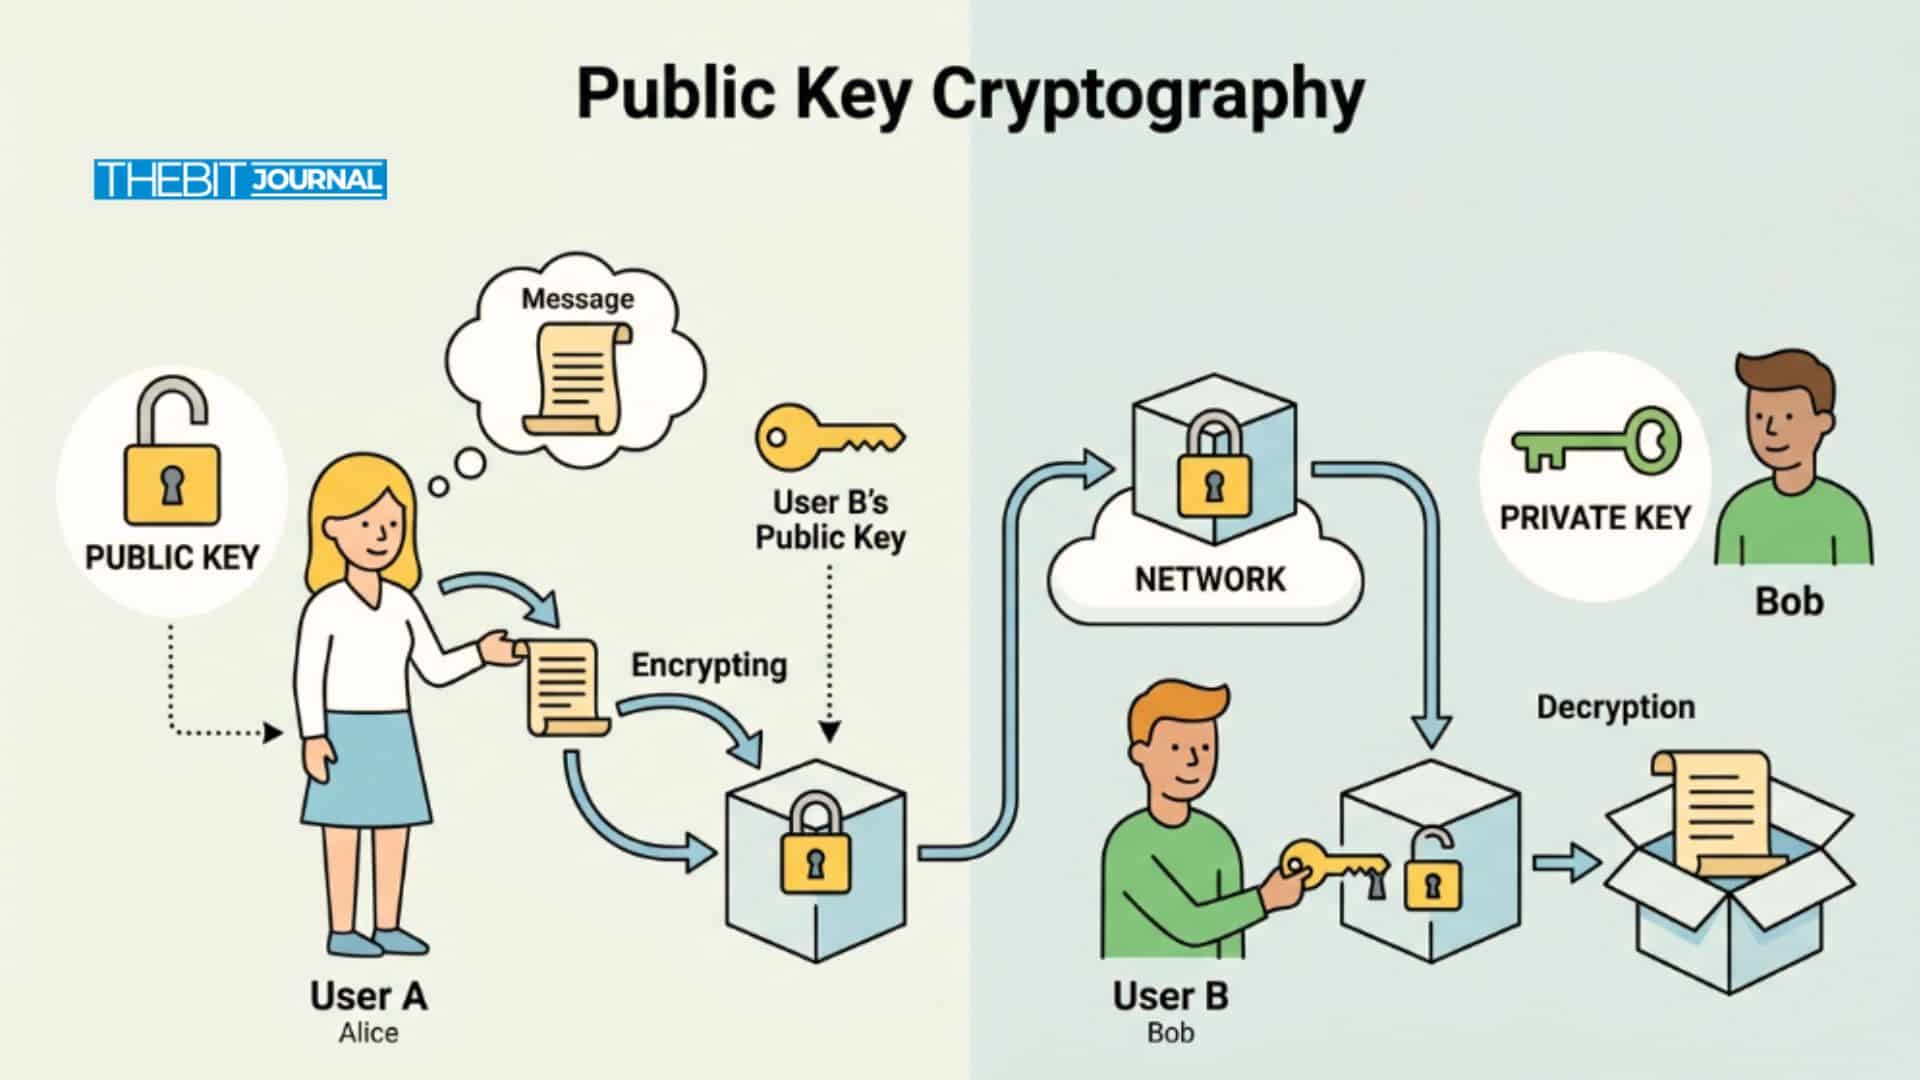
Public key cryptography forms the backbone of modern digital security. By employing a key pair—one public and one private—it enables the encryption, signing, and authentication of data without requiring parties to share secrets in advance. The public key serves as the shareable half of this pair: anyone can see or use it, but only the holder of the matching private key can unlock encrypted data or verify signatures intended for them.
This mechanism makes secure, trusted communication and transactions possible across the open internet and blockchains, powering everything from HTTPS websites to cryptocurrency wallets. Virtually every secure web session, mobile app connection, and blockchain transaction conducted today depends on this technology.
Public key cryptography effectively solved the internet's foundational trust problem by eliminating the need for secret key exchange. As Whitfield Diffie and Hellman's groundbreaking 1976 invention demonstrated, each user generates a unique key pair, shares only the public half, and keeps the private half secret. Data encrypted with the public key can only be decrypted by the corresponding private key, and signatures created with the private key can only be verified with the public key. RSA, introduced the following year, and elliptic-curve cryptography (ECC), developed in the mid-1980s, became the two algorithm families that carried this model into widespread commercial use—protecting web traffic, email, software updates, and eventually cryptocurrency networks.
How It Works
Public key cryptography, also called asymmetric encryption, relies on mathematical algorithms in which key pairs are computationally linked. Each pair consists of a public key (shared openly) and a private key (kept secret).
According to MDN Web Docs, "Public-key cryptography is a cryptographic system in which keys come in pairs. One key (the private key) is kept secret while the other is made public."
A useful analogy is a mailbox: the public key functions as the mailbox address (anyone can drop in a letter), while the private key is the mailbox key (only the owner can retrieve the contents).
The two keys serve distinct, complementary functions:
Encryption and Decryption: Anyone can encrypt a message using a public key, but only the corresponding private key can decrypt it. In email or messaging applications, users publish their public key so that contacts can encrypt messages readable only by the key holder.
Digital Signatures: A user signs data with their private key, and others verify the signature using the public key. Every cryptocurrency transaction relies on a private key to generate a digital signature, which the network then verifies with the public key. The same principle applies to signing documents or software packages—anyone can confirm authenticity using the signer's public key.
These roles are complementary: in encryption mode, the public key encrypts and the private key decrypts; for signing, the private key signs and the public key verifies. This design allows public keys to be widely published—even attached to emails or hosted on websites—while private keys remain locked down.
Public Key vs. Private Key
Security experts emphasize that while a public key can be freely shared, the private key grants full access to any funds stored at the associated public address. In blockchain networks, the public key functions like an account number: all participants see it, or a hashed version of it, as a wallet address. The private key, by contrast, must be guarded at all costs, because anyone possessing it can impersonate the rightful owner.
Encryption, Signatures, and Blockchain
Public key cryptography underpins many everyday technologies. When visiting a secure website (HTTPS), a browser fetches the server's public key certificate and uses it to establish an encrypted channel. Only the server's private key can decrypt the session keys the browser sends, preventing eavesdropping or tampering. The website's public key is freely available as part of the TLS certificate, while the matching private key remains on the secure server.
In email, protocols such as S/MIME and PGP allow anyone to encrypt messages using a recipient's public key; only the recipient can open them with their private key.
Passwordless login systems (FIDO2/WebAuthn) also rely on public key cryptography. A user's device generates a public/private key pair for each site, and the site only ever sees the public key. Security bodies note that modern authentication becomes phishing-resistant when private keys remain uncompromised. FIDO standards employ standard public key cryptography techniques to provide phishing-resistant authentication: no password is transmitted, and the user instead proves possession of the private key.
In blockchain systems, public keys play a critical role. A cryptocurrency wallet generates a key pair, derives a wallet address from the public key (typically by hashing it), and shares that address so others can send funds. The public key serves as an address for receiving cryptocurrency or data, while the private key grants control over the associated digital assets. When a user initiates a transaction, the wallet signs it with the private key, and the network verifies the signature using the public key—proving the transaction originated from the account holder. With major blockchain networks processing millions of transactions per day, this verification loop runs continuously and at global scale.
Beyond cryptocurrencies, public keys are fundamental to digital certificates and identity systems. Organizations issue certificates that bind public keys to individuals or servers, allowing third parties to trust that a key genuinely belongs to the claimed user. Certificate Authorities (CAs) manage these certificates and can revoke compromised keys. This framework, known as Public Key Infrastructure (PKI), enables verification of public keys through trusted CAs.
Why Public Keys Matter—and How They're Secured
Because public keys can be used by anyone for encryption or verification, they are widely shared—sometimes even published in global directories or recorded on blockchains. Security nonetheless depends entirely on the private key remaining secret. Modern cryptographic systems such as RSA and elliptic-curve cryptography (ECC) are designed so that deriving the private key from the public key is computationally infeasible. Due to one-way mathematical functions (trapdoor functions), it is effectively impossible to recover a private key using only the public key.
However, all such guarantees rest on careful key management. A stolen or leaked private key compromises the entire security model: data intended to remain private becomes exposed, and signatures become forgeable. Organizations must store private keys in Hardware Security Modules (HSMs) or secure vaults, rotate keys regularly, and employ strong algorithms, as highlighted by Encryption Consulting.
The Post-Quantum Shift
A major trend in 2026 is preparing public key cryptography for the advent of quantum computers. Classical public-key algorithms such as RSA and ECC rely on mathematical problems—integer factorization and discrete logarithms—that a sufficiently powerful quantum computer could solve. This has given rise to a "harvest now, decrypt later" concern: adversaries can collect and store encrypted data today with the expectation of decrypting it once quantum capabilities mature, meaning the threat timeline effectively precedes the arrival of large-scale quantum machines. NIST warns that administrators should begin transitioning to new standards capable of withstanding quantum attacks. In August 2024, NIST released its first three finalized post-quantum encryption standards—FIPS 203 (based on CRYSTALS-KYBER for key establishment), FIPS 204 (based on CRYSTALS-Dilithium for digital signatures), and FIPS 205 (based on SPHINCS+ for stateless hash-based signatures).
By 2030–2035, many agencies plan to deprecate RSA-2048 and ECC P-256. The meaning of a "public key" may consequently change: future public keys will be larger and based on new mathematics, but the core principle remains unchanged—one key public, one key private. Today's public keys are already growing in size to prepare for post-quantum cryptography (PQC). A new PQ signature scheme may produce 2,420-byte signatures and 1,312-byte public keys, compared to 256-byte RSA signatures.
Expert Insight: Trust via Public Keys
Cybersecurity experts emphasize that public keys enable trust without requiring parties to share secrets. Every blockchain transaction uses a public key to verify that the signature was indeed created by the holder of the corresponding private key. The public key itself does not need to be secret; it serves as proof of identity.
This is why attackers cannot steal funds merely by knowing a public key. Even though the public key, wallet address, and all transaction signatures are visible to everyone, funds remain safe as long as the private key stays private.
Public key cryptography also shifts trust to mathematics and standards. Government and industry bodies maintain algorithms and protocols ensuring that public keys genuinely belong to their claimed owners. Organizations such as the FIDO Alliance now encourage replacing passwords with public-key-based "passkeys"—cryptographic credentials designed to prevent phishing.
Additional resources from IBM and Ledger Academy provide further context on how asymmetric cryptography secures blockchain ecosystems.
Conclusion
A public key is the non-secret half of an asymmetric encryption key pair, intended to be shared openly. It allows anyone to send encrypted data to the key holder or verify signed messages. Public key cryptography powers everything from HTTPS to cryptocurrency, enabling secure communication without pre-shared secrets.
Modern security standards and research continue to evolve around public key cryptography—including the development of post-quantum-safe algorithms and phishing-resistant authentication. The fundamental principle endures: the public key is public, the private key is private, and this duality keeps data secure by design. As a result, public key cryptography remains the indispensable foundation for online security in 2026, providing scalable, trustworthy encryption and digital signatures across both the web and blockchain ecosystems.
Glossary
Asymmetric Cryptography: A cryptographic system using key pairs (public and private). Data encrypted with one key can only be decrypted by the other.
Private Key: The secret half of an asymmetric key pair, kept confidential and used to decrypt messages or create digital signatures.
Digital Signature: A cryptographic proof generated with a private key that can be verified with the corresponding public key, ensuring data integrity and origin.
PKI (Public Key Infrastructure): A system of digital certificates and authorities that bind public keys to entities.
Post-Quantum Cryptography: New cryptographic algorithms designed to resist quantum computing attacks, which threaten many current public-key algorithms.
Frequently Asked Questions
What is a public key used for?
A public key encrypts data and verifies signatures. Anyone can use it to send encrypted messages to the key holder or to confirm that a message signed with the corresponding private key is authentic.
How does a public key differ from a private key?
A public key is shared openly; a private key is kept secret. The public key enables encryption and signature verification, while the private key enables decryption and signing.
Can someone derive my private key from my public key?
In modern cryptography (e.g., RSA, ECC), deriving the private key from the public key is computationally infeasible. Security relies on one-way mathematical problems, meaning the private key cannot be computed even when the public key is known.
Why are public keys important in blockchain?
In blockchains, public keys (or their hashes) serve as wallet addresses and identify accounts on the network. When sending a transaction, the sender signs it with their private key; other nodes use the public key to verify the signature, ensuring only the rightful owner authorized the transfer.
What happens if a public key is compromised?
Since public keys are designed to be shared, there is no harm in them being known. System security depends on the private key remaining secret. Even if someone obtains a public key, they cannot decrypt data or forge signatures without the corresponding private key.
Disclaimer: This article is for educational purposes and does not constitute financial or investment advice. Any information about cryptographic protocols or future standards should be independently verified.

