Ledger Says All Confirmed Cases in Suspected $87 Million Drain Tied to Reseller CryptoBilis
Key Takeaways
- •Ledger stated that every confirmed case from the wallet-draining incident involves devices bought through Southeast Asian reseller CryptoBilis, and that its own systems and direct sales channels remain unaffected.
- •Onchain investigators traced more than $86 million in suspected stolen funds across Ethereum, Tron, and Bitcoin, though Ledger has not confirmed the amount or identified the cause of the losses.
- •Investigator YFarmX reported the thief laundered proceeds through Tornado Cash, Zcash's shielded pool, and stablecoin conversions, with Tether freezing 10 million USDT while roughly 15,475 ETH, 203 BTC, and 10 million USDD remain unrecovered.
- •CryptoBilis has confirmed it ceased all hardware wallet sales, and Ledger is reminding authorized resellers to source products only through official channels and never restock returned items.
- •Ledger advised CryptoBilis buyers not to set up unused devices and to move any funds to a newly generated seed phrase, since a tampered device could expose the original recovery phrase to attackers.
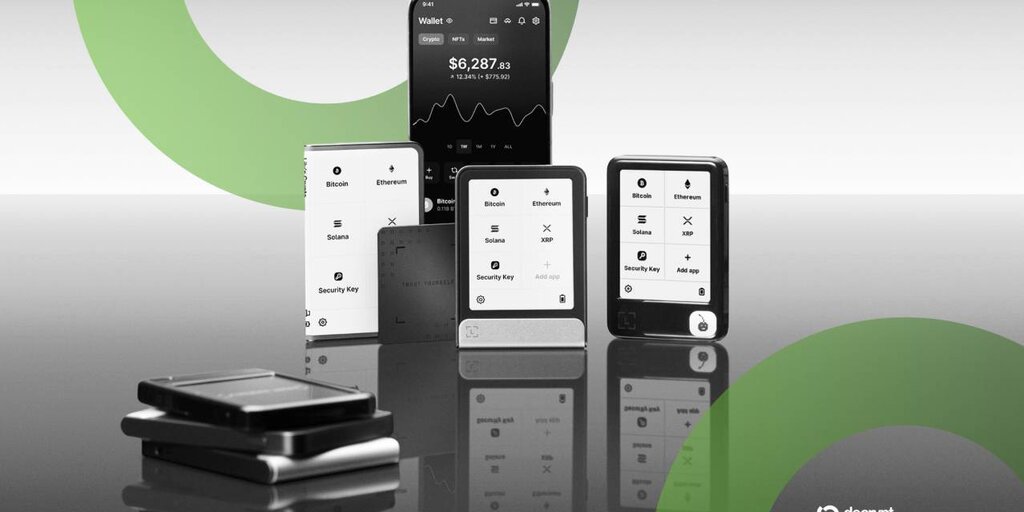
Ledger said every confirmed case in last week's wallet-draining incident involves hardware wallets sold through Southeast Asian reseller CryptoBilis, and that its own systems and direct sales channels remain unaffected, according to a 72-hour update posted on Sunday.
"The volume of impacted devices is limited," the Paris-based hardware wallet maker said, adding that it is working with relevant authorities and reaching out to affected users. It said CryptoBilis has confirmed it has ceased all sales of hardware wallets.
72 hour update on reseller CryptoBilis incident 🔽 As the investigation continues, we are working with relevant authorities. The volume of impacted devices is limited. We know this is concerning, especially for those directly affected, and we are reaching out to impacted users.Emphasis added
— Ledger (@Ledger) October 11, 2026
Ledger began investigating on Friday after users in Southeast Asia who bought devices from CryptoBilis reported losing funds. Onchain investigator Specter traced more than $86 million in suspected thefts across Ethereum, Tron and Bitcoin. Ledger has not confirmed that figure or said what caused the losses.
Hardware wallets such as those made by Ledger are designed to keep users' private keys offline, but security researchers have long cautioned that devices obtained outside official channels can be tampered with before they reach buyers. A modified device can expose the recovery phrase a buyer generates during setup — the 24-word sequence that controls access to the wallet's funds.
Onchain investigators YFarmX said they had sent Ledger a list of more than 450 drained wallets. According to their analysis, the thief pushed 2,810 ETH through coin mixer Tornado Cash in three runs, moved the withdrawals through Zcash's shielded pool, a privacy feature that conceals transaction details, and withdrew about 3.28 million USDC into three fresh wallets, which Circle could freeze.
The thief also converted 15 million of the stolen USDT into USDD, a stablecoin Tether cannot freeze, before swapping 51 million back into USDT and sending about 4.23 million USDT to Binance deposit addresses, YFarmX said. Tether froze 10 million USDT on the first day, while 15,475 ETH, 203 BTC and 10 million USDD remain out of reach, according to the firm. Its findings have not been independently verified.
An X user named Johannes has claimed to have found tampered Ledger devices in Europe after buying two devices from retail stores. He said both had "identical modifications (such as additional cables and an LTE module)," and called on Ledger to issue a product recall.
Those claims have not been independently verified, and Ledger's update said all confirmed cases so far involve CryptoBilis devices. Johannes said he is sending the second device to Ledger for analysis. Decrypt has reached out to Ledger for comment on the European reports.
Reseller controls
In its update, Ledger said it is reminding authorized resellers and distributors to source products only through authorized channels and "never to restock returned products."
It also warned users against buying from unauthorized resellers, where "the risk of buying suspicious, counterfeit or modified devices is important."
The company said it is reviewing reseller controls and advancing hardware protections, and called on others in the industry to work with it on supply-chain and anti-tamper practices.
Ledger repeated its advice that CryptoBilis buyers should not set up unused devices, and that anyone who has should move their funds to a new seed phrase on a device bought from Ledger. The guidance reflects how the suspected risk works: if a device was modified before sale, a seed phrase created on it could already be known to an attacker, leaving funds exposed until they are moved to a newly generated phrase.
It also warned that scammers may try to exploit the incident, saying it "will never call you, DM you, or ask for your 24-word recovery phrase."

