Solana's Firedancer Adds 1 SOL Burn Fee for Bug Reports After AI-Assisted Submissions Surge
Key Takeaways
- •Jump Crypto now mandates that security researchers burn 1 SOL, worth about $100, before Firedancer bug bounty submissions can qualify for reward payments.
- •The burn fee is non-refundable and applies even to duplicate, invalid, or out-of-scope reports, though submissions without proof of the burn may still be reviewed.
- •The policy follows an audit contest held from April 9 to May 9 that generated 809 submissions from 162 researchers, yielding 127 unique findings with nearly half of valid reports duplicating earlier ones.
- •Jump researcher Ishan Bhatt said AI agents likely helped produce almost every contest submission, and the review queue peaked at 299 open reports with most duplicates arriving more than three days late.
- •Bounties are doubled through November 20, and reports specific to Solana's newly launched Alpenglow upgrade qualify for triple rewards of up to $300,000 for critical findings.
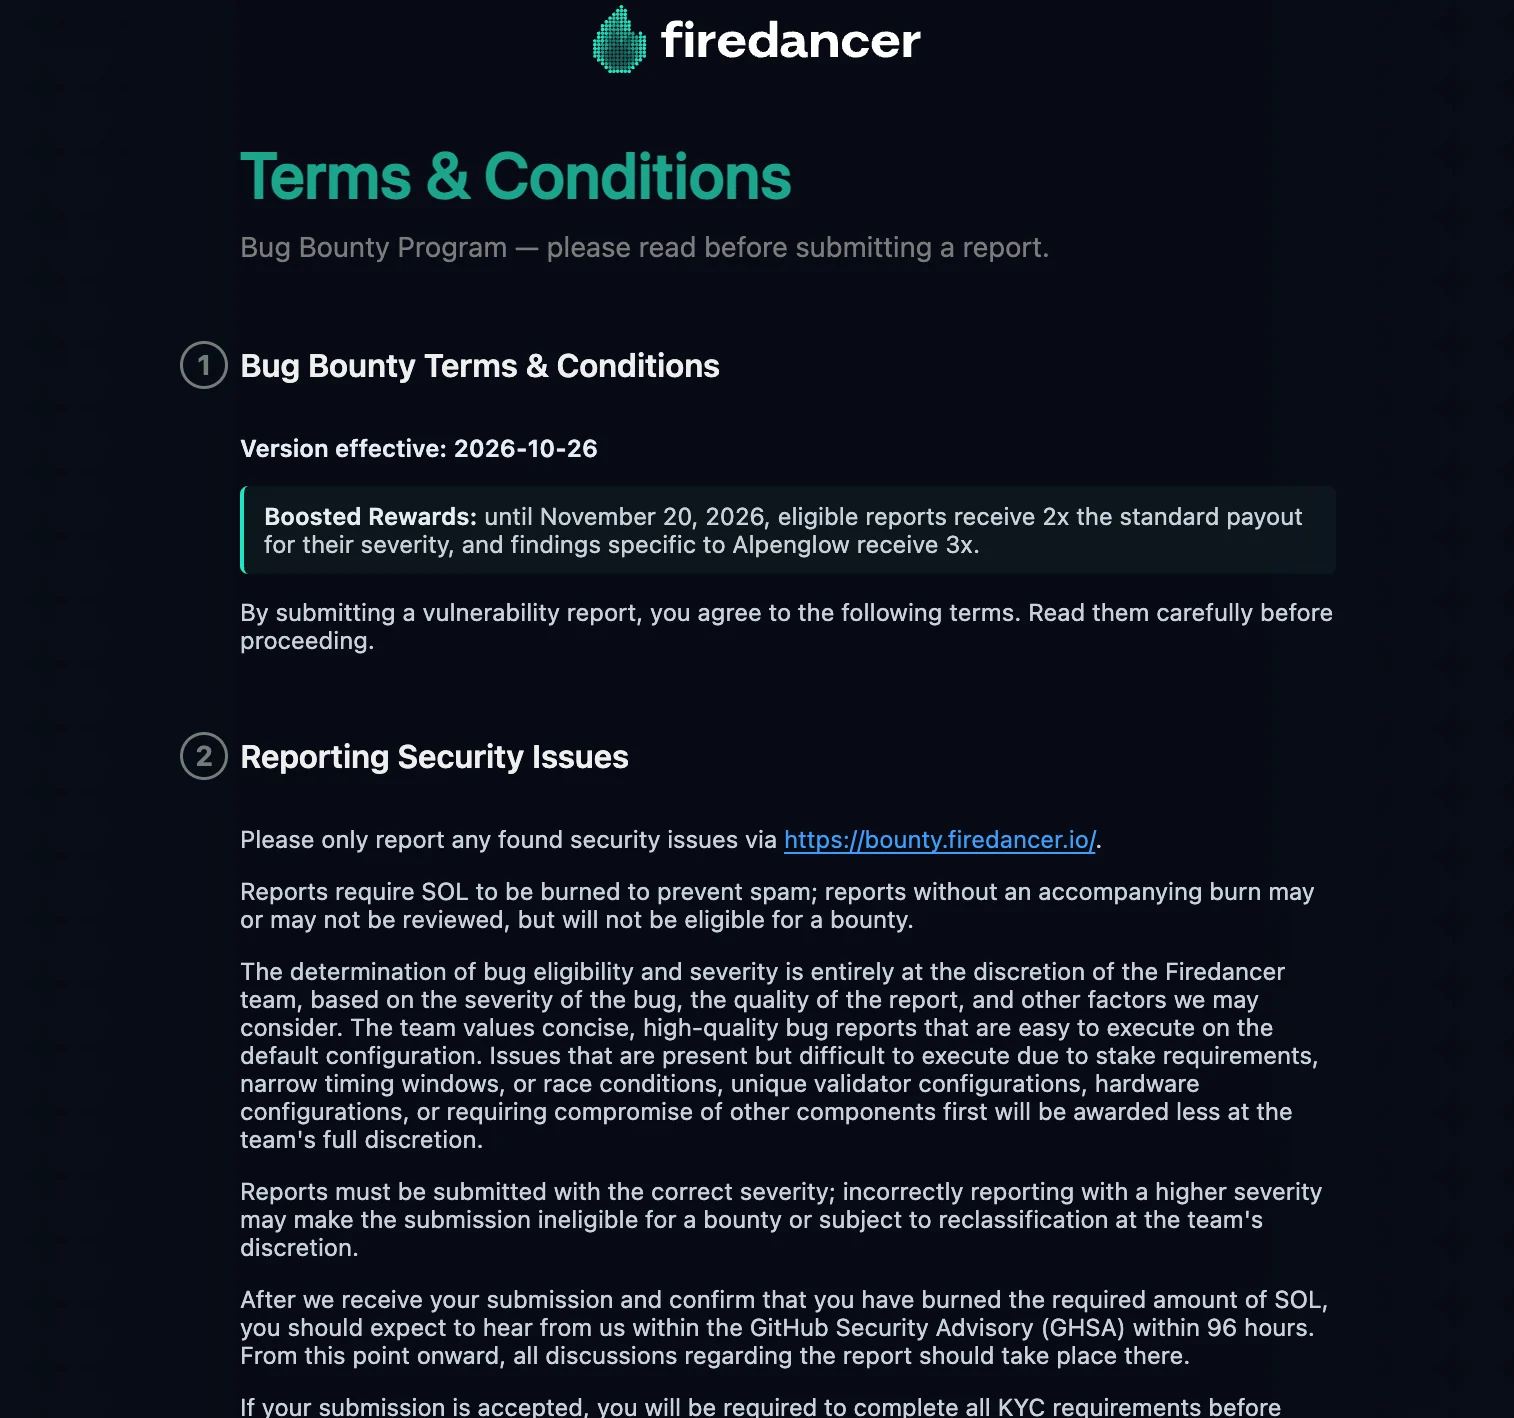
Jump Crypto has introduced a 1 SOL burn requirement for security researchers submitting reports to Firedancer, its independently developed Solana validator software. The token, worth roughly $100, must be destroyed before a report can qualify for a bug bounty reward.
Under terms updated October 26 on the program's official website, the fee is non-refundable, even when a report turns out to be a duplicate, invalid, or outside the scope of the program. Submissions filed without proof of the burn may still receive a review, but they cannot receive rewards.
AI-Driven Backlog Behind the Change
The new rule follows an audit contest held from April 9 to May 9 that was designed to surface vulnerabilities in the validator software. Jump received 809 submissions from 162 researchers, which yielded 127 unique security findings. Nearly half of the valid reports repeated issues that others had already identified.
Ishan Bhatt, a researcher at Jump, said AI agents likely helped produce almost every submission. The review queue peaked at 299 open reports, with 80% of duplicate findings arriving more than three days after the original. The backlog shows the tradeoff AI tooling introduces for security teams: candidate reports can be generated at scale, but each one still has to be reviewed before any bounty is paid. Separately, plans for Solana validator operations in Hong Kong were announced this month.
A Cost for Untested Claims
Jump says the burn requirement creates a financial cost for submitting untested claims. The fee goes to an address that cannot spend the tokens, meaning Jump collects no payment. Its previous contest charged $100 per report and limited entries to one per researcher per day.
Researchers must explain how to reproduce each flaw, and the new submission platform restricts main report sections to 3,000 characters. Jump expects to contact eligible researchers within 96 hours after confirming both the submission and the token burn.
Triple Rewards for Alpenglow Bugs
Firedancer is offering twice its usual bounty amounts through November 20. Reports specific to Solana's Alpenglow upgrade qualify for triple rewards, with critical findings eligible for up to $300,000, although Jump determines final payments.
The incentives follow the mainnet launch of Alpenglow, Solana's new voting system, on October 21. The upgrade changes how validators reach agreement on Solana transactions, and Jump is encouraging researchers to examine the new code while the higher payments remain available — giving researchers a fixed window to probe newly launched mainnet code under elevated terms.
Additional Context
Firedancer runs alongside Agave, another Solana validator client, a pairing that means Solana's consensus does not rest on a single validator implementation. Jump said its software secured about 15% of Solana's staked SOL as of October 16. A separate Solana trading bot wallet breach reported on October 26 involved user wallets and was not tied to a known Firedancer flaw.
The audit previously uncovered a transaction scheduling error that could cause Firedancer to process payments out of order and disagree with other validators. Jump says the new reporting rules are designed to reduce review delays while keeping serious security findings eligible for rewards.
Source: CoinCentral

