Casino Pages Found on INEC Website 142 Days Before Nigeria’s 2027 Elections
Key Takeaways
- •About 28 casino and gambling pages were found live on INEC’s official domain, including material published under the WordPress author name Ajuma Achor.
- •The voters.inecnigeria.org subdomain was reported to display unrelated Russian text and an SSL certificate tied to a different newly registered domain, suggesting a possible subdomain takeover.
- •INEC’s ICT director said the BVAS accreditation devices still run on Android 10, but the commission uses a customized build and says it has no plan to upgrade the operating system before 2027.
- •The site intrusion is consistent with a wider pattern in which an Indonesian-linked network placed casino content on government websites across multiple African countries for search-ranking gain.
- •INEC has been urged to conduct a public forensic audit of publishing accounts, vendor credentials, and subdomains, and to have ngCERT investigate the voter subdomain claim.
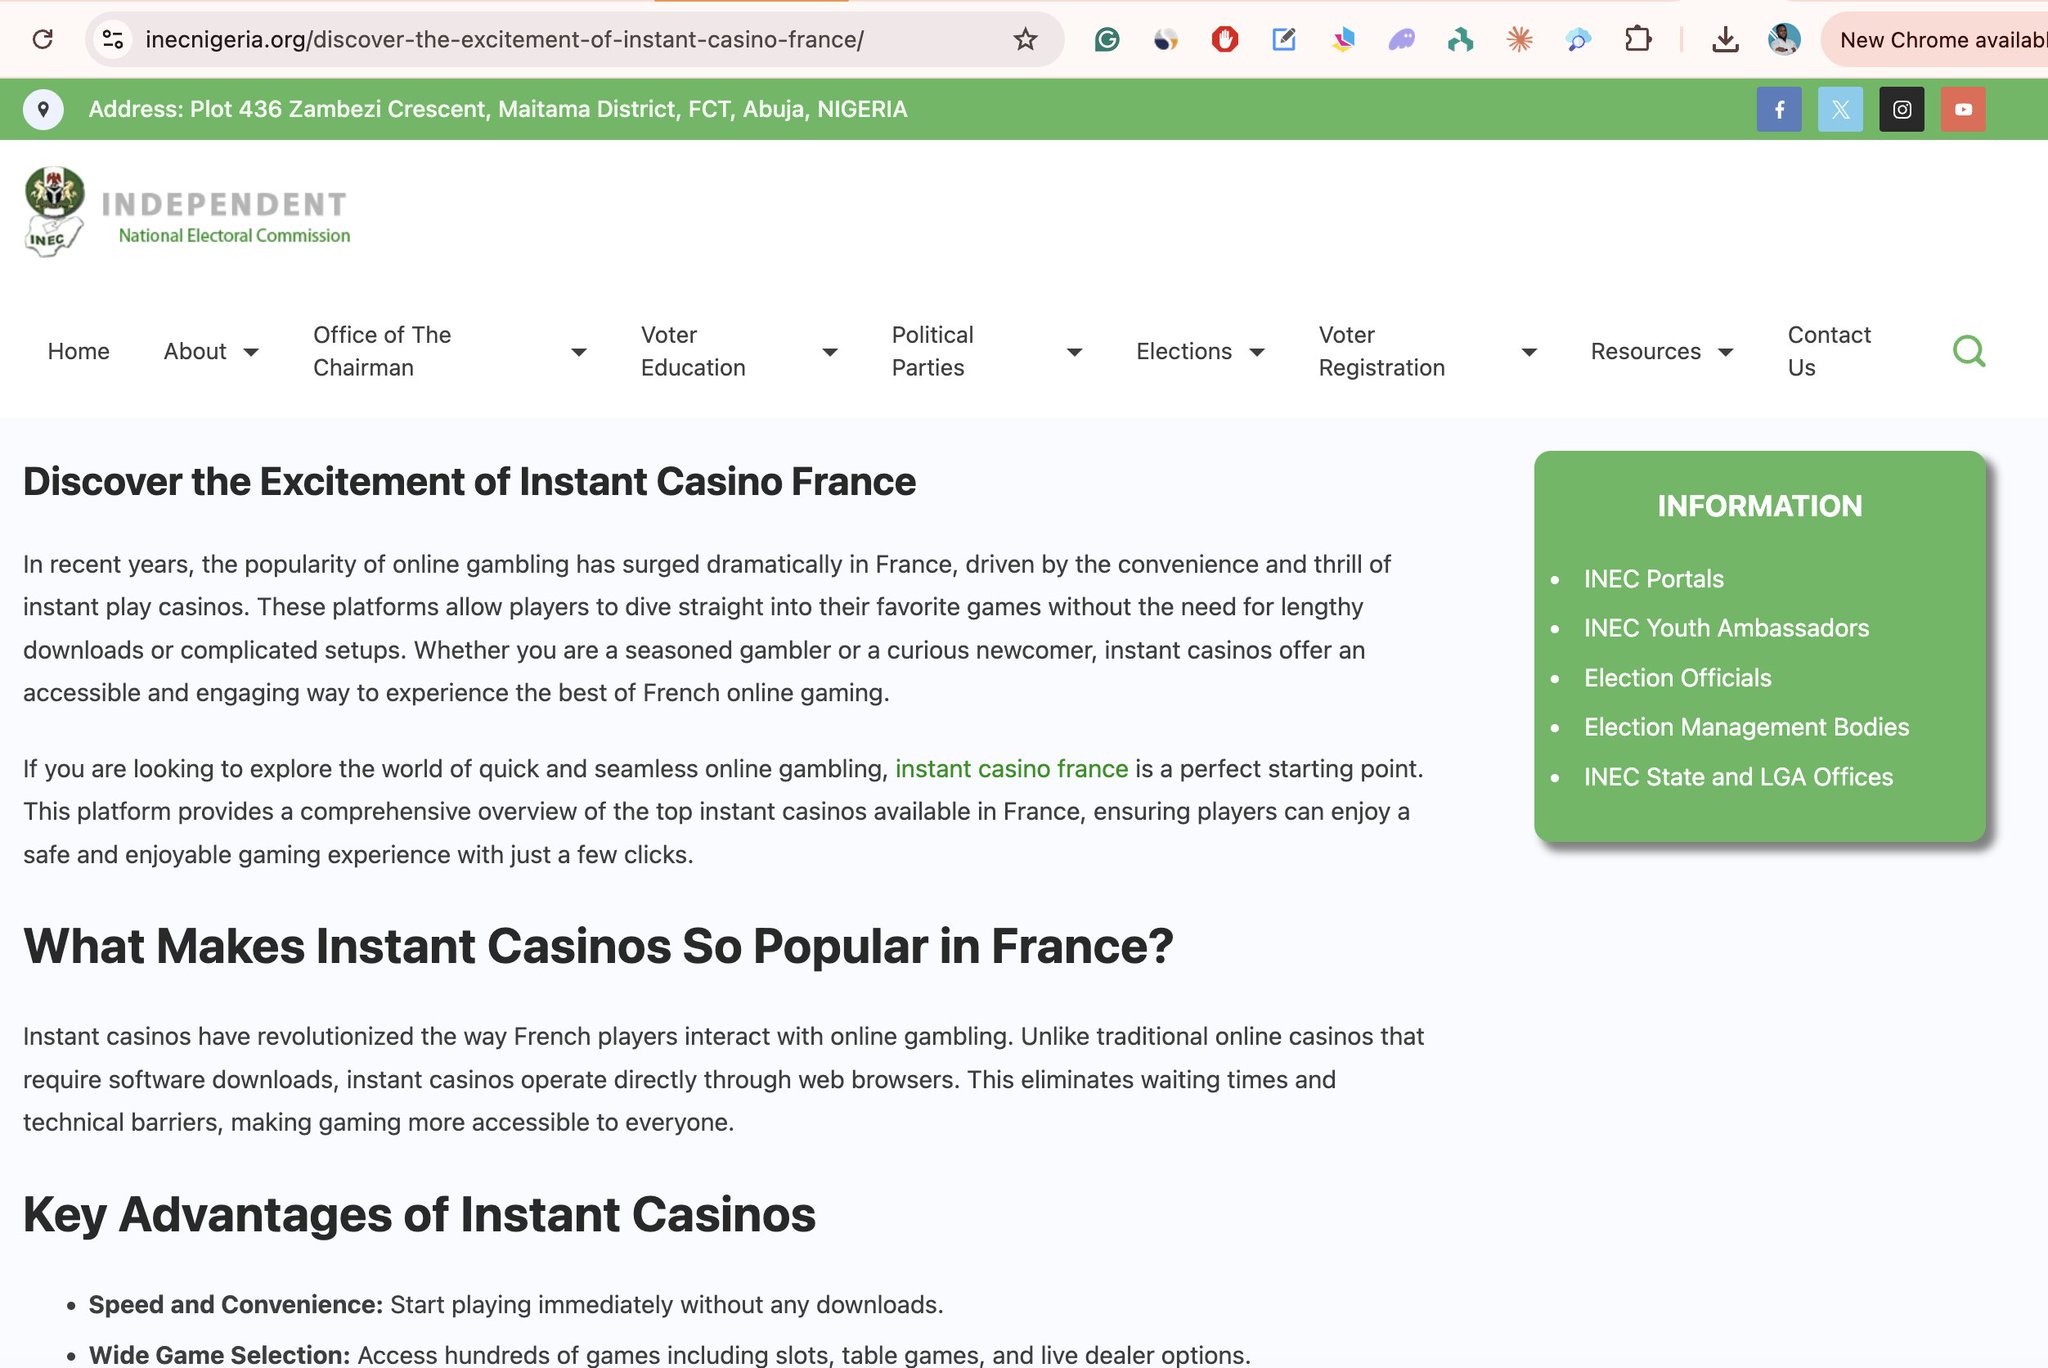
One hundred and forty-two days before Nigerians go to the polls to elect their next set of leaders in the 2027 General Elections, casino pages were found on the official website of the Independent National Electoral Commission (INEC), the body that will conduct and announce the election results.
The discovery was made late on August 26, 2026, 23 days before the next scheduled bye-elections and only weeks after INEC’s own ICT director confirmed that the country’s core accreditation devices still run on Android 10.
On August 26, data researcher Mundus documented roughly 28 casino and gambling articles published directly on inecnigeria.org. These were not outbound links, but live pages on the official domain, including Czech-language casino explainers, “instant casino France” promotions, and similar search-engine bait clustered under the WordPress author name Ajuma Achor.
The same name appears in professional records as Head of Marketing at Interra Networks, an ICT firm that has previously supplied contact-centre and other services to INEC. Mundus outlined two possibilities: a long-compromised publishing account that no one audited, or someone with legitimate access using it for paid SEO placements. Either way, credentials that can quietly publish dozens of gambling pages can, in principle, publish a fabricated results notice or a false announcement when the country is watching.
A second problem was flagged the same night: voters.inecnigeria.org was reported to be serving unrelated Russian text and an SSL certificate belonging to a newly registered, unrelated domain, a classic sign of a possible subdomain takeover. Such takeovers typically occur when a DNS record still points to a third-party service that has since been decommissioned, allowing anyone who re-registers the account to take control of the address. A voter-facing host in that condition is not merely a cosmetic issue. It sits next to the channels citizens use to check registration and to treat official digital services as authentic.
The African syndicate already inside government websites
The INEC website takeover fits a campaign recently documented by Techpoint Africa: an Indonesian-linked network that planted casino content inside about 20 government websites across 16 African countries, including Nigeria, Egypt, Kenya, Uganda, Ghana, and South Africa. The objective was search ranking. Google trusts established official domains more than new gambling sites. Hide a casino page inside a government CMS, and the operators inherit that trust. Google itself moved against this pattern in 2024, when its “site reputation abuse” spam policy began targeting third-party content published on high-authority domains to exploit their search ranking.
Researcher Chris Nwobi of Zend Cybersecurity Threat Labs said the attackers did not need elite exploits. Outdated software and internet-exposed administration panels were enough. A gambling-focused presence had already been observed on Nigeria’s Federal High Court site as early as November 2024. By May 2026, multiple Nigerian agencies were serving Indonesian-branded content, including “SLOT88” notices. GitHub commits during Indonesian working hours, local support numbers, and QRIS payment rails pointed back to the same ecosystem. The July dossier named institutions such as NILDS, NEMA, NAERLS, the EFCC, and the Federal High Court. INEC was not on that original list. If this attack is confirmed to come from the same threat actor, it would mean the electoral commission has now joined a club it should never have entered.
The syndicate’s motive appears commercial, but that does not make the foothold harmless. Once an attacker or an insider can write to an official CMS, the same channel can be used for disinformation, phishing pages designed to harvest voter data, or a timed disruption on election day.
Weeks before the website incident, INEC Director of ICT Dr. Lawrence Bayode confirmed on Arise TV that the Bimodal Voter Accreditation System still runs Android 10, the version the devices shipped with in 2021. Google ended mainstream security support for that release in 2023. Bayode said the commission is not relying on the operating system alone. According to him, the machines use a locked-down, customized build, additional INEC-controlled security layers, and isolated apps for accreditation and result upload. He also said there is no plan to change the OS before 2027, because a newer Android version would require hardware upgrades, including more RAM, that could slow the devices. BVAS is not a new experiment: it replaced the smart card reader used since 2015, and under the Electoral Act 2022 it is the machine that accredits voters electronically and feeds polling-unit result images to the INEC Result Viewing portal (IReV), whose delayed uploads during the 2023 presidential election became a major complaint in the court challenges that followed.
Critics, including former Vice-President Atiku Abubakar and independent cyber analysts, argue that an unpatched base system still widens the attack surface. Public Android bulletins have listed critical remote-code-execution flaws affecting Android 10. A customized build inherits part of that risk if the underlying kernel and libraries are not independently maintained. BVAS devices capture fingerprints and faces, match them against the register, and transmit polling-unit results. A compromised unit could, in theory, alter cached accreditation logs or result files before they leave the polling booth.
The August Osun mock accreditation already produced failures that INEC blamed on older voter records generating high similarity scores. Those incidents were technical. The credibility problem they feed is political: the same institution now accused of hosting casino pages on its public site is asking the country to trust devices whose operating system has been unsupported for three years.
Election integrity does not begin on the night of the count. It begins with whether citizens believe the register is clean, the accreditation devices are under control, and official websites cannot be silently rewritten. Publishing access on inecnigeria.org has not been shown to be tightly inventoried. A voter subdomain in an insecure state shows that even citizen-facing infrastructure can drift. Android 10 on BVAS shows that the 2021 hardware purchase was treated as a finished product rather than a system that needs a security life cycle.
Voter data is the most sensitive asset in that stack: biometrics, addresses, polling-unit assignments, and the historical register. Casino pages on a WordPress site are not the same thing as a dump of the national register. They are evidence that write access and perimeter control were weak enough for outsiders, or insiders with leftover credentials, to plant content at scale. The weaknesses that let a gambling network ride African government domains can be reused by actors who want votes, not bets.
The website and the BVAS are different machines. A blog login cannot, by itself, rewrite a result file inside a handheld device. An unsupported Android build does not prove that SEO operators touched the register. The danger is the pattern: neglected official sites, long vendor relationships, and election technology bought as hardware instead of as a platform that must be patched until the last ballot is counted.
What INEC must do before 2027
Nigeria’s next national test is already dated. The presidential and National Assembly contests are scheduled for January 2027. Deleting casino slugs, if they are still live, is the minimum. It is not the story.
INEC needs a public forensic audit of every publishing account, every vendor credential, and every subdomain. It needs ngCERT, Nigeria’s national computer emergency response team, to investigate the voters subdomain claim. It needs to say whether Android 10 devices can be defended at national scale, or whether the 2021 fleet is technical debt wearing an election logo. And it needs to report what, if anything, was accessed besides SEO pages.
Until those answers are provided, the casino articles on inecnigeria.org are not an embarrassing footnote, but a warning issued 142 days too close to a crucial presidential election.

