Compromised private key behind roughly $2 million theft from Fetch.ai and NuNet
Key Takeaways
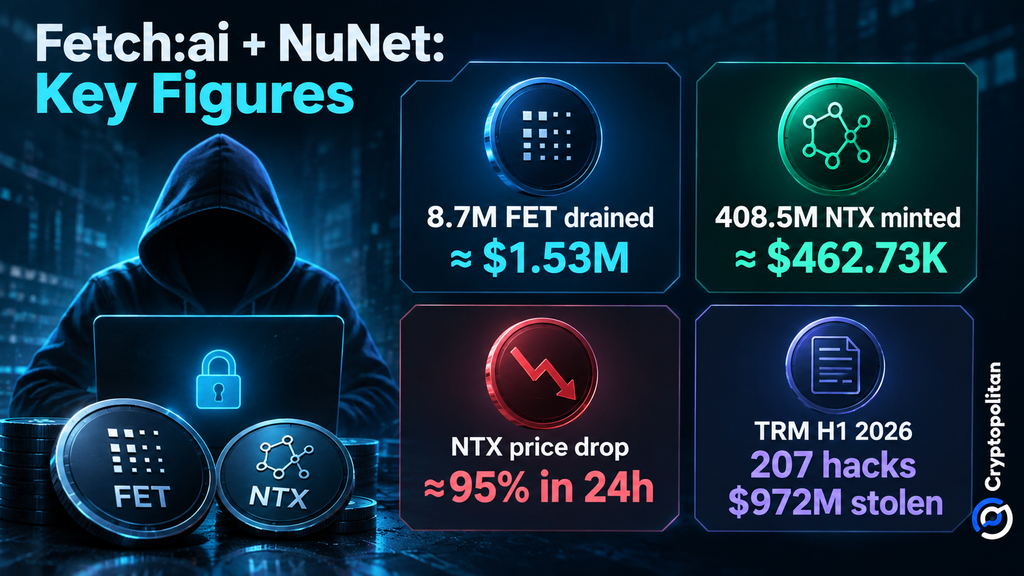
- •An attacker used compromised signing credentials to drain about 8.7 million FET (approximately $1.53 million) from a Fetch.ai converter and to mint 408.5 million NTX (around $462,730) without authorization, with both actions linked to the same wallet.
- •SlowMist reported that the TokenConversionManagerV3 contract relied on a single ECDSA signature from one externally owned account and lacked limit checks or on-chain burn and lock proof verification, allowing the drain once the authorizer key was compromised.
- •Fetch.ai worked with SingularityNET to deactivate affected wallets and contracts, paused AGIX-to-FET conversions as a precaution, and published a preliminary on-chain tracing the attack from the compromised key to the attacker's cash-out wallets.
- •NTX dropped almost 95% in 24 hours to around $0.000066, hitting an all-time low of $0.00004075 on September 20, because unauthorized minting diluted existing holders, whereas FET faced no comparable supply shock.
- •Industry data shows infrastructure and operational compromises accounted for only about 15% of the 207 hacks recorded by TRM Labs in the first half of 2026 but roughly 76% of the $972 million in stolen funds, placing this incident in that smaller, high-impact category.
An attacker has stolen around $2 million from infrastructure connected with Fetch.ai and NuNet, in a pair of incidents that security firms linked to the same attacker wallet. Preliminary analysis by Fetch.ai found that the attacker used compromised signing credentials to gain access to the infrastructure, with on-chain monitoring flags raised as the exploit unfolded on September 19, 2026.
Measured against an estimated $2.85 trillion crypto market, a $2 million theft may appear minor. What makes this case notable that compromised privileged credentials gave the hacker access to critical infrastructure, highlighting how weaknesses in key management can spill across connected systems even when the underlying token contracts themselves are not compromised.
The same wallet drained FET and received the NTX mint
According to PeckShield, the hacker siphoned off a total of 8.7 million FET, valued at approximately $1.53 million, and minted 408.5 million NTX without authorization, worth around $462,730. FET is the native token of Fetch.ai, while NTX is the token of NuNet.
Blockaid separately observed about $1.56 million in FET removed from a converter, along with approximately $452,000 in newly minted NTX. That brought the total value of the wallet cluster to about $2.01 million while the attack was ongoing, and a follow-up post connected the NTX mint to the same receiving wallet.
🚨Blockaid detected an ongoing exploit on @Fetch_ai on Ethereum. The same exploiter wallet then received a large NTX mint from the @nunet_global deployer account. $2.01M so far ($1.56M FET drained from the converter + ~$452k NTX minted) across the cluster. Attack still… — Blockaid (@blockaid_) September 19, 2026
Post: https://x.com/blockaid_/status/2101426221825348095?ref_src=twsrc%5Etfw
NuNet is part of the same broader AI-crypto ecosystem; CoinMarketCap describes it as the second spin-off from SingularityNET.
The weak point was privileged authorization
The evidence presented so far does not establish that a single key was responsible for both projects. Based on Fetch.ai's preliminary analysis, the signing key was likely compromised, while on-chain analysis implies that NuNet's minting key may also have been compromised.
In its analysis, SlowMist reported that the TokenConversionManagerV3 relied solely on an ECDSA signature — the cryptographic signature scheme Ethereum uses to authorize transactions — from a single externally owned account to authorize the conversionIn() function through which the FET was drained. The function did not implement a checkLimits(amount) control against the transaction, and it did not check whether burn or lock proofs were available on-chain. The drain happened as soon as the authorizer key was compromised, since a legitimate signature was all that was required to empty the converter's FET balance.
Fetch.ai said it worked with SingularityNET to deactivate affected wallets and contracts. A later update said no Fetch.ai contracts were then at risk and that AGIX-to-FET conversions — AGIX being SingularityNET's token — had been paused as a precaution. The company also published an on-chain analysis of the exploit on ASI:One, tracing the attack from the compromised signing key to the attacker's cash-out wallets.
An on-chain analysis of the exploit is now available on ASI:One. It traces the attack from the compromised signing key to the attacker's cash-out wallets. This is not the final analysis. Read the report: Together with @SingularityNET , we have deactivated… — Fetch.ai (@Fetch_ai) September 20, 2026
Why NTX cratered while FET did not
The two tokens responded in distinct ways because the attacks had different effects on supply. The FET incident involved the theft of previously issued tokens, while the NTX incident generated hundreds of millions of unauthorized tokens, compromising supply integrity and adding extra selling pressure. The distinction matters because minting new tokens dilutes existing holders directly, whereas a theft of project-held tokens does not change the total supply.
According to CoinMarketCap, NTX was trading around $0.000066, down almost 95% over the previous 24 hours, after hitting an all-time low of $0.00004075 on September 20. FET's situation was not complicated by a comparable supply shock.
A familiar industry pattern
The direct loss is modest, but the attack method fits a much larger industry pattern. TRM Labs recorded 207 hacks and $972 million in losses in the first half of 2026. Infrastructure and operational compromises accounted for only about 15% of incidents but roughly 76% of stolen funds — meaning a relatively small share of incidents accounted for the bulk of value stolen. The Fetch.ai and NuNet theft falls into that smaller, high-impact category, with the losses traced to compromised privileged credentials.
CoinGecko's 2026 security report tells a similar story. Infrastructure and supply-chain breaches caused more than $1.8 billion in losses between January 2025 and July 2026, while private-key compromise remained a major failure point.
Cryptopolitan reported a similar pattern in June, when Humanity Protocol said exposed private keys contributed to losses of up to $31 million, and its H token fell as much as 90%.
Fetch.ai says the investigation remains open, and the analysis it has published is explicitly not final. The next questions are how the credentials were compromised, whether Fetch.ai has rotated or replaced all affected privileges, and how NuNet handles the unauthorized NTX still linked to the attacker.
Source: Cryptopolitan

