Apple tightens Mac data access as AI agent privacy concerns mount
Key Takeaways
- •Apple will require very explicit user action before macOS apps can obtain Full Disk Access, which can expose files, emails, messages, and browsing history.
- •The policy change followed complaints from an Inc columnist who said Meta's Muse AI agent read his private messages without Full Disk Access being enabled, a claim Meta disputed by saying the access requires users to opt in.
- •Muse previously faced a separate security issue when Meta strengthened its warnings after a researcher discovered an SEV-2-classified flaw that could potentially have exposed a user's virtual machine, emails, and files.
- •Enterprise research points to trust as a commercial constraint, with 60% of large enterprises having slowed, stopped, or postponed AI deployments over reputation, regulation, and trust concerns.
- •Investment in AI models and platforms is forecast by Gartner to rise from $39.3 billion in 2025 to $64.3 billion in 2026, while Capgemini estimates AI agents could create up to $450 billion in value by 2028.
Apple will impose stricter controls on macOS applications that request sweeping access to data stored on a Mac, the company announced on October 2. The decision follows complaints about Meta's Muse AI agent and underscores a broader question now facing the software industry: how much access AI agents should have, and how that access should be disclosed and governed.
What Apple is changing about Full Disk
In its developer update, Apple said Full Disk Access can expose files, emails, messages, and browsing history because it bypasses the safeguards that normally protect app data.
“Going forward, we will introduce additional controls to ensure that users who genuinely wish to grant an app this extraordinary level of access can only do so with very explicit user action,” Apple wrote. The company added that “as AI agents become increasingly capable and autonomous, the risks associated with this level of access will grow substantially.”
As Reuters explained, the issue carries particular weight on Mac computers. iPhones and iPads are designed to keep applications separated from one another as a default protection, whereas an application on macOS that holds the Full Disk Access privilege can reach a much broader range of user data.
How quickly the new controls arrive, and how many steps the explicit consent flow requires, will shape how much the change adds in practice—details developers and users alike will be watching for.
Why Muse drew the complaints
The change followed complaints from Inc columnist Jason Aten, who said Muse read private messages on his Mac even though he had not enabled Full Disk Access. His account drew a public dispute from Meta.
Meta spokesperson Andy Stone said on X that access to Apple Messages is opt-in: users must first enable both Full Disk Access and the Messages connector, and they can revoke that permission at any time.
Whichever account is accurate, the dispute spotlights the disclosure question at the center of Apple's move: whether users can tell, at a glance, which permissions an agent is exercising.
This is not the first security controversy for Muse. According to Cryptopolitan's earlier reporting, Meta tightened Muse's security warning after a researcher discovered a flaw, classified SEV-2, that could potentially have given an attacker access to a user's virtual machine, emails, and files.
Why agents need the keys to everything
The tension is built into agentic AI: the more useful an agent becomes, the more access it may need.
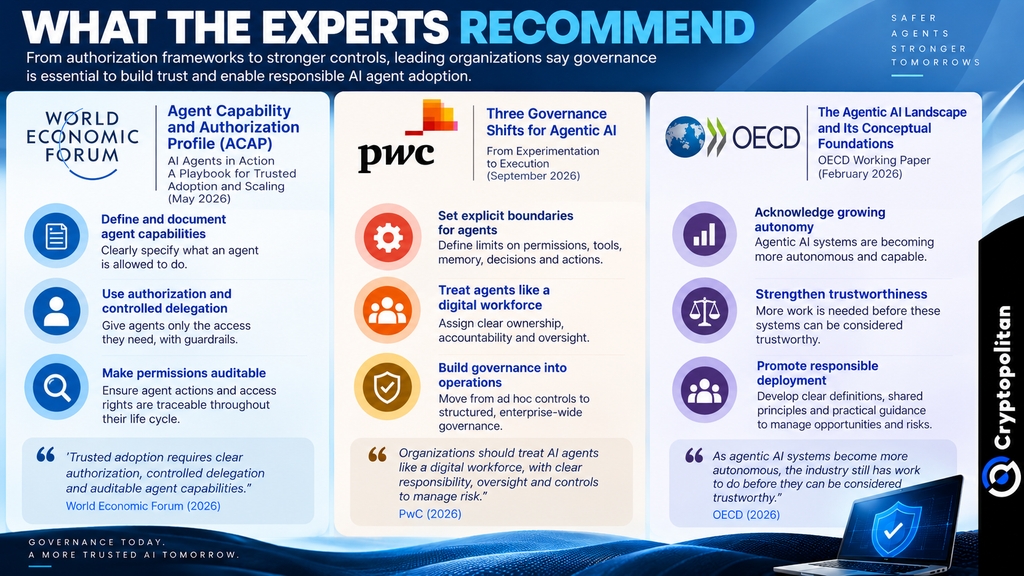
The World Economic Forum recommends an Agent Capability and Authorization Profile to define what an agent can access and what it is allowed to do, with the aim of making those limits easier to track and enforce.
PwC takes a similar view. It argues that companies should manage AI agents like a digital workforce, with clear ownership, access based on specific tasks, and limits on what the agents can do on their own.
The OECD strikes a more cautious note. In its report, the organization says agentic AI is still evolving and that more work is needed before such systems can be considered trustworthy.
That guidance is advisory rather than binding; for most users it takes effect only through the permission systems built into their operating system—the layer Apple is now tightening.
Trust is turning into a commercial constraint
These concerns are already shaping how businesses deploy artificial intelligence. Research by FTI Consulting found that 60% of large enterprises have slowed, stopped, or postponed AI deployments because of reputation, regulation, and trust issues.
A SAS report also points to a trust gap: 76% of respondents trust generative AI, compared with 66% who trust agentic AI. Companies that invest in trustworthy AI methods were 15 times more likely to see a high or good return on those efforts.
A great deal of money rides on that trust. Gartner forecasts that investment in AI models and platforms will rise from $39.3 billion in 2025 to $64.3 billion in 2026. Capgemini estimates that AI agents could create up to $450 billion in value by 2028, even though only 2% of companies have fully implemented AI systems.
Friction now, broader adoption later
Apple's tighter controls may add friction, but clearer, revocable permissions could also make users more comfortable granting agents meaningful access. As agentic AI moves from experimentation into everyday use, permission design is becoming part of the product itself—not just a compliance issue.

